Home Depot Breach 43M loss posting on LinkedIn

I just read an article on LinkedIn about the negative impact caused by the recent Home Depot breach. Here are my thoughts about how all the 2014 breaches should change some C level and Information Security paradigms. These could cause a major C suite thought shift and maybe even a large paradigm thought shift in how our profession thinks about the skills and talents really needed by Information Security professionals.

Note – I know this opinion will not resonate well with some CISO’s – Major IT departments continue to hire CISO’s that have little to no security background. Hackers and blackhats are associated with organized crime and IMO until we put more of an emphasis on the word SECURITY in the CISO title and until CISOs stop walking a tightrope by always trying to compromise and keep the business happy by letting the business need trump the security need (“ok, don’t patch that extremely vulnerable system I understand your business need not to” ) the crooks will continue to win.

Also, it appears that too many companies are basing their CISO hiring decisions on the candidate’s business acumen. Wouldn’t it be better to focus on how well the candidate knows how to fight and deter criminals?
I’m not saying CISO’s don’t need to understand the business I am saying that a stronger focus should be on how much the CISO knows about criminals and crime fighting. I also realize that thought would take a major paradigm shift in the thinking of the C suite.

The Insider Threat is Alive and Well – a summary taken directly from Raytheon’s How to Build an Insider Threat Program (2014) …

Aspects of human nature further complicate matters: Well-intended managers resist any notions of “their people” doing “bad things.” They screened them. They hired them. They work with them side-by-side and – if they’re good bosses – have developed a genuine interest in their career development and even personal happiness. In addition, one of the most critical elements in building a high performing team is trust, so anything thaWhite Hatt can have a negative impact on that trust needs to be very carefully analyzed and explained before being implemented.  This disposition is not about being gullible, we all have white hat syndrome at times. It’s about being a helpful manager – and a decent person.
But it would be imprudent to completely abandon a sense of cautionary oversight, as there has been a steady flow of news reports about insiders doing harm to their organizations. They range from probably the most notorious of incidents – Edward Snowden’s carefully plotted leaking of sensitive NSA documents after downloading 1.7 million files – to possibly the funniest (except for the company in question): A software developer for a U.S. critical-infrastructure company literally outsourced his job by sending his log-in credentials to a Chinese contractor, so he could get paid six figures to surf Reddit, post Facebook updates, shop on eBay and watch cat videos all day2.  While the latter anecdote has generated considerable amusement, it underscores the reality that internal threats pose serious risks: 53% of organizations have experienced an insider cybercrime incident, according to the 2013 U.S. State of Cybercrime Survey from the CERT Insider Threat Center at the Carnegie Mellon University.  So who are the users who pose threats? In all cases, they have authorized access to the network and their co-workers and managers are usually shocked that they would do such a thing.  Clearly, tech departments need the support of their leadership to do what plant managers and foremen did in the 1950s: Watch. Audit. Intervene. Prevent.

Regardless of the user’s full time or contractual status, you want to look for classic “tip-off” behaviors which can lead to trouble, e.g. the clear taking of proprietary information NinjaHackerwithout need or approval; expressing increased interest in matters unrelated to defined duties; and connecting to the network remotely from unusual places at unusual times, having access to machines that they really don’t need access to, constantly seeking for elevated privileges, to list a few examples from the FBI profiling studies.  Without a program in place to stop these individuals, organizations stand to lose an estimated $412,000 on average per incident.
In many organizations, a “we trust everyone to do the right thing” mindset too often prevails, and data points abound, such as 50% of employees who leave a company admitting to taking proprietary data,  to show why this is highly questionable logic.

Another issue is with internal rule benders who conclude that the added layer of protections are either unnecessary and/or overly alarmist and/or present too many inconveniences for them to deal with. They consider themselves and their work as above it all, and decide on their own as to when to follow security protocols – and when to circumvent them. As they grow more comfortable with the latter, they choose it as their “default” setting, doing things such as sending proprietary information outside the company “walls” without encryption, logging onto systems that they should not have access to, elevating other person’s access rights because security doesn’t understand the person’s real need, etc.  They love external drives and USB sticks, because these tools make it nearly impossible to distinguish risky behavior from harmless, work-related shortcuts. In fact according to a recent survey conducted by Voltage Security 50% of network users admitted to having bypassed security controls to complete a task more quickly and easily. Internal Rule Benders make up 15% of treat actors who have caused or committed a breach of their organizations’ data.  Senior executives are disinclined to acknowledge that the worst is, indeed, possible: “We trust the people we hire” and they perform a valuable role. We do not want to promote a culture of suspicion.  These Senior executives need to realize that Trust but Verify is a good mantra for them to start living by.

oopsIt’s too difficult. It’s too costly. There’s no imminent crisis. “Status quo”                                  is working out just fine. Then like, Target, Home Depot and many others they                      find out that it’s not, after it’s too late. 

On our team how can we implement items that allow us to do the following?

  • CERT’s “Common Sense Guide to Mitigating Insider Threats” has emerged as an industry standard for program implementation. Among its recommended actions:
    • Launching a security information and event management (SIEM) system to log, monitor and audit user activity.
    • Detecting activities outside the users’ normal scope of duties via phone/network logs, etc.
    • Regularly reviewing accounts to verify that all are still active and necessary.
    • Ongoing auditing of user accounts created and passwords provided.
    • Requiring all system administrators to change passwords when a fellow administrator leaves his or her job.*
    • Monitoring and controlling remote access from all end points, including mobile devices.
    • Incorporating threat awareness/prevention policies into comprehensive termination policies.
    • Developing a baseline of “normal” network device behaviors.
    • Inventorying IT assets and routinely assessing their present-day role and relevancy.

Remember:

If you don’t go looking for trouble you will never find it.  

But, Trouble will find you / your Organization

How do we get back to this future in a technological workplace?

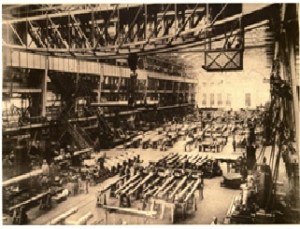
In the classic factory of the 1950s, managers strolled from their offices on a floor that towered over plant activity, closely observing whether shift crews below were doing what they were supposed to do. Because employees knew the eyes of a supervisor may be upon them at any time, they were less inclined to cheat the system – such as slipping any of the company’s property or product into their pockets, or sabotaging a machine out of spite. Thus, the business was protected. And what was good for the business was good for everyone involved: the bosses, the investors and, yes, the workers.  Said another way, it is good for business and for organizations to keep one rotten apple from spoiling the bunch.
factory

A day in the life of a senior Cyber Security Incident Responder


The day was proving to be an exciting one for team Havoc, the Company’s cyber Red Team, as the L2 report he had just read showed that 4 of the core company servers were vulnerable to a very common exploit.  Glacier, the Red Team leader, was evaluating the report and figuring out how he was going to communicate this to the Global IT leaders.  It was important to not just inform IT of the vulnerability, but to have recommended solution sets to present that were reasonable and that would allow them to be able to
remediate the vulnerabilities.  Glacier was on his second read through of the report whencyber hacker he noticed a section that mentioned end user data on the systems being encrypted.

“Hey Hammerhead come over here.” Hammerhead is the teams best Wintel expert. “What’s up?” “Take a look at these systems and check out what is happening with the data on the shared drive.  I’m thinking we’ve already been hacked and have a serious issue here.  What do you think?” “Oh man Glacier, it looks like we have an active ransomware attack, maybe using something like Cryptowall. ”

Glacier immediately contacts NightShade, the Cyber Incident Response Team (CIRT) coordinator and asks her to get the team assembled.

While the above scenario does happen more often than we would like it to, thankfully it is not an everyday occurrence.  Most days consist of conducting risk assessments on malware and zero-day events, investigating abnormal system behavior, and investigating employee or corporate security reports of suspicious activity. Each of these events has to be analyzed and assessed quickly, all the while knowing that each of the actions decided upon will be second guessed by arm chair quarterbacks across corporate IT leadership.  Let’s say the Incident Response (IR) team makes a decision to patch systems based on their initial intelligence gathering and risk analysis. If any of these systems have a production failure due to the patch, pushback from IT immediately begins and argument over the need and criticality of the patch ensues. Even when the actions taken, such as having corporate executives change their passwords, are less impactful to productivity than leaving a Second Guessingbuilding due to a fire alarm, second guessing by business leaders is inevitable. Even though the IR team’s decisions are rooted in cyber intelligence followed by an appropriate risk analysis, they are frequently told they are overreacting.

The business and IT leaders who do this second guessing often ask that in the future when these decisions are made they be made by group consensus.  This thinking shows a complete lack of understanding on how fast cyber-attacks can move.  For example:  When the blaster worm came out as a zero day event it took down Fortune 500 companies around the globe in less than 15 minutes. The other issue with this type of reasoning is that these business and IT resources, while highly intelligent, have limited knowledge of cyber security and what it takes to prevent or quickly remediate data breaches. This fact has been made obvious by the long line of large data breaches all in companies that had limited Cyber Security resources or that did not listen to the ones they did have.

The same business and IT leaders who are doing the second guessing of Cyber Security professionals most likely read the first paragraph of this paper with thoughts that it is silly and bizarre for Cyber Security IR teams to use nicknames.  Experienced IR professionals understand that hackers and fraudsters are highly intelligent and capable of conducting social engineering research to find the names of IR members so they can track those names on chats and systems in an effort to disrupt response capabilities.  In the past, law enforcement professionals have had the bad guys call police stations pretending to be a hospital where their wife or husband had just arrived after being in a car accident. it is very possible that cyber attackers would try some of the same tactics to disrupt IR response capabilities.  There are many IR teams that only have one UNIX or one Wintel resource and having them not engaged would cause a large negative impact to team operations.  So, not only should IR teams use nicknames but these nicknames should also be treated as restricted data.

So, after that interlude, let’s get back to a day in the life of a senior IR professional.   As with most jobs, coffee is the beginning of the day. While drinking their coffee, the IR professional reviews a variety of Cyber Intelligence sources to determine potential impact to the current employer.  On some days this leads into the intelligence gathering and risk analysis work discussed above, on other days it leads to a check through emails to make sure that the Level 1 (L1) or Level 2 (L2) Security Operations Center (SOC) did not have any urgent findings for immediate handling.  If there are no urgent needs in email, then a variety of L1 and L2 SOC reports are reviewed and analyzed and items of interest are followed up on as needed.  Being a student of Stephen Covey’s 7 habits and the Corporate Athlete methods, lunch is something lite and is followed by a walk or quick work out.  After lunch, the senior IR professional performs a quick check-in with each of the team members to see what items they are working on and to make sure that moral is high. This is followed by another quick email review to make sure nothing urgent has come in from Corporate Security, the company’s See Something – Say Something campaign, or either of the SOCs.   Assuming nothing needing attention has come in, the IR professional brings up the SIEM dashboard to conduct a Quality check of the work being done by the L1 and L2.  This often leads to some phone calls or a meeting with their team leaders to reinforce Standard Operating Procedure (SOP) items that are not being correctly followed.  The end of the day usually consists of going through all the emails that have had to sit while the daily tasks were completed.

The Cyber Security CIA explained via Calvin and Hobbes

Leave it to my son Kody, who is starting his Cyber Security career to come up with this novel way to explain the CIA triad for Cyber Security.

In InfoSec terms, CIA refers to Confidentiality, Integrity, and Availability. To illustrate how these principles work, let’s look at Calvin and Hobbes.

Calvin and Hobbes create a club called the “Super-Secret-No-Icky-Girls-Allowed” club. During their very first treehouse meeting, they draft a document entitled “member list” and write the names “Calvin” and “Hobbes” on the list. This list is the club’s most valuable asset so Calvin and Hobbes need to maintain the CIA of the asset. The confidentiality of the list is critical as the exposure of the secret member list would cause the entire super-secret club to lose its purpose. The integrity of the list is also important to ensure that unauthorized modifications of the list can’t be made. It would be terrible if Susie’s name were to make it on the list of if Calvin’s name were to be removed. Lastly, the availability of the list is important. When the club meets to have their secret meetings, they need the list do roll call and to ensure that those in attendance are listed.

So now that we’ve got the idea, we can explain how CIA works for business assets. The confidentiality of the asset is necessary to ensure that only those with appropriate privileges and appropriate need can see the asset. The integrity of the asset is necessary to ensure that the data has not been changed and, if it has, a log of changes is kept. The availability of the asset is necessary because it is not of any value if no one can interact with it for its intended purpose.

Compliance does not Equal Security

When I read items like this:

Agarwal said NoMoreRack is now in the process of certifying itself this time as a Tier-1 merchant, even though the number of credit and debit cards it processed in 2013 placed it squarely in the Tier-2 range.

I get frustrated.  While I understand that Compliance is necessary and is important companies still need to understand that being compliant does not mean you are secure! There is more to it than that.  In too many cases Compliance is just a check box that makes senior management feel better about the overall state of organizational security.

Fun Story about UC Cyber Warfare Game

Ok, so I wasn’t going to share this but I sort of think its
pretty neat. My friend Quinn and I started an urban legend story at
the University of Cincinnati from my classes first cyber warfare
event years ago. One of my current students just posted the following item in a class I am teaching. This is a story that is really about the first
Cyber Wargame that I ran at UC as part of my Information Security
Course. Quinn was the defender and I believe Karl Hart was the
attacker – it was a great event. What is even greater is that is
has now taken on UC “legendary” status. :-)
============================================

I am reminded of a story my Computer Networking teacher, Mr. Tom Moore, gave to us one day in class. He spoke of a game they played, I dont remember whether it was at UC or his workplace, but he said that they would divide IT professionals into 2 teams, one “hackers” and one that
protected data. He was on the hackers team. Well the protectors
were allowed a certain amount of time to design security for the
system they were trying to protect, and there after the hackers got
their shot. Well the hackers tried and tried to break the security
through their hardware but to no avail. Finally, Mr Moore was on a
break and happened to walk by the room the protectors were in (they
were set up in different rooms of a building) and realized no one
was in there. He tried the door but it was locked. However, another
faculty member, unaware of what was going on, walked by and Mr.
Moore asked her to unlock the door. She did and he notified his
team who came and stole all the equipment they had. They then broke
into the machine, got the data, and won. He used the Bill Gates
quote “if I can get access to your computer I will own everything
that is on it” and it stuck with me. This story is a prime example
of having physical controls in place, and not just one. It is
important to make sure your equipment and data are both safe from
harm.

Why Is It?

Why is it that Internet Crime statistics continue to show that for the criminally inclined internet crime is a very viable and fast growing field?

Why is it that millions of dollars are stolen from end users who simply fail to pay attention to the basics of Information Security like strong pass-phrases and “don’t click the link”?

Why is it that in March of 2010 there was a breach of University student’s personally identifiable information (PII) that numbered over 3.3 million identities being stolen?

Why is it that in 2012 there was a breach of over 6 million IDs from the state of South Carolina IT Infrastructure?

Why is it that online banking theft is at an all time high with thefts against mid size business and metropolitan areas taking center stage?

Why is it that even though unheard amounts of information is being stolen daily that non-cyber security professionals are still very vocal in explaining to experts in the field of cyber security why passwords, pass-phrases, encryption and other basic controls don’t work and are too cumbersome?

  •  Yet in most breach cases if basic information security controls and best practices like defense in depth would have been in place and followed the breach would not have occurred

Why is it that the non- Cyber Security professional’s opinions on what Cyber Security controls are important are often given more weight than the Cyber Security professional’s opinions within an organization?

Why is it that Senior IT and Business managers within an organization still won’t listen to the Cyber Security professionals they employ when it comes to building and maintaining an effective security and control infrastructure?

Why is it that Cyber Security professionals still don’t have the voice they need within most corporations (Government, Public and Private) to actually protect the organization’s data?

Why is it that blame for failure to protect corporate data is quick to be placed on the shoulders of Cyber Security professionals who weren’t listened to in the first place?

Why is it that as experts we really do have the knowledge and ability to protect sensitive corporate data but in most organizations we are not given the power to do so?

Why is it that rhetorical questions are not answered?

© Kevin L. McLaughlin – properly cited use is encouraged

The Talent Within

11/8/2012

In his book “Topgrading: How leading companies win by hiring, coaching and keeping the best people” (2005) Dr. Smart talks about how important it is for a company to not only hire A level talent but then keep and retain them through the years.  I have had the good fortune to work for a company that was very good at this and not only did they hire and retain A players they had a very good internal training program to make sure that the A players they hired were trained and taught the new roles they moved into in order to lessen the knowledge gap and learning curve for the new position.  In this environment efficiency, streamlining, being agile, having solid and well followed processes were the norm.  Needless to say this is a good environment for a talented knowledge professional to work and grow in.  The basic idea was to hire and surround yourself with great and talented A performers and then allow them to make decisions and drive systemic change ongoing.   To me this process of hiring smart and talented people and then promoting them as next step openings become available makes a lot of sense.

Unfortunately, throughout my professional travels what I have often observed is that even in companies with great training programs and who espouse the philosophy of growing talent from within there is a strong psychological tendency to seek outside for the next professional with a briefcase (J  that’s an old joke about how your own company or organization never views you as an expert or qualified candidate, even if the rest of the nation views you that way),  and bypass their internal talent pool.

What a lot of the VPs and directors who are hiring do not realize is that if you have an A player on your staff who is one level lower than the position you are filling they will succeed if you put them in the position, even if they have some knowledge gaps, that is pretty much what A players do.     I know, a lot of you who are reading this are scratching your heads and thinking about all the times a resource is promoted beyond their ability and wondering how that fits in.  The answer is simple, they weren’t an A player or they were an A player who, inherited all B and C players and wouldn’t aggressively cull the herd.

Both competent B and lower level C performers, especially ones that are non-performing destroy any possibility of creating a high performing team.  These lower talented professionals don’t create this less than successful environment on purpose, it is just that they really don’t understand the higher level connections and thought process of the A player and they end up being more of a hindrance and distractor to overall success than they are a key component to the accomplishment of overall success.

There is research study after research study that shows if you have 90+% A players in your management ranks you will be extremely successful in your team and corporate endeavors.  That being said I continue to scratch my head when I see organizations with A level talent who are available to move into a next tier open position go out on a public search to fill the position.  A level talent is very hard to find, and to think that you are going to be able to search outside and find it more readily than you can identify and find it in the work force that has been with you for an extended period of time is simply naive.  What typically happens is that an experienced director or VP is brought in from the outside and they end up after a short amount of time showing that they are a B or low level C talent.  Even more mind boggling to me is that none of the people who were responsible for bringing this less than high end performer into the organization want to admit to making a bad hire so they live with the impact an under talented manager brings to their organization.    The outcome of such a decision is that their true A players are driven from the organization and they take their talents to a competitor, where they are typically extremely successful working and managing at a level their previous employer would not promote them into.

Organizations really need to take a good look at their talent retention programs and give them more than just lip service and they also need to come to the realization that all forced ranking systems do is allow for the B and C players  figure out sly ways to sabotage their talent pool of A players.  Like Ken Blanchard says, organizations should help all of their “employees earn a grade of an A”,  in my opinion the Blanchard approach to talent management will more readily allow you to identify and distinguish between the A, B and C players in your talent pool.

© Kevin L. McLaughlin, probably cited re-use is acceptable

In Cyber Crisis

We are a country in crisis in regards to adopting adequate Information Security practices.   I am not an alarmist but when I review the Cyber Security update that my team compiles and sends out a couple of times per week and see multiple breaches in every update and when I see reports like the one conducted by Adam Dodge or the Verizon Report that show steady amounts of information security breaches every year I have come to believe that we are a country in Cyber crisis.

Puzzling to me is that for some reason we, as a society have decided that the safeguarding of personal information should be a soft skill that is done by committee instead of by the certified and trained professionals we hire into Information Security roles.  Interesting enough the members who are sitting on the committees making Information Security and data protection decisions are often times not Information Security professionals.   To use an analogy – it seems that instead of deferring to our qualified “pilots” we are allowing the passengers to fly the airplane without providing them flight instructions first.  If we really want to protect our corporate data then we cannot  keep making Information Security decisions, such as should Personally Identifiable Information (PII) be encrypted, by consensus.  We also need to see the cost benefit with hiring Information Security professionals and then listening to their advice. Due to a large data breach the State of South Carolina recently ended up paying $12 million that could have been put to better use; they could have asked any of us Information Security professionals if the data they lost should have been encrypted at rest and in transit to save $12 million.  Instead (and this is pure conjecture on my part) they probably made the decision not to do so by a consensus of the CIO and other IT professionals, none of whom were trained Information Security professionals.

In my personal life I refrain from telling my accountant how to complete my taxes or from telling my surgeon where and how to make her surgical cuts.  It is time, if we truly want to protect our data or the data we are entrusted to safeguard, for our communities to start adapting the course of action that Information Security Professionals and Information Security Standards advise. If we don’t start allowing our certified and trained professionals to specifically mandate how organizational PII, Intellectual Property, e-PHI, collectively referred to as restricted data, should be protected we will continue to allow this data to be lost or stolen.

While there is no silver bullet that will prevent 100% of this type of data loss most experienced and certified information security professionals know that there are many controls and safeguards we can put in place, if allowed to do so,  that will minimize the loss of restricted data.

Note – my use of the words Information Security is synonymous with Information Assurance.

© Kevin L. McLaughlin, probably cited re-use is acceptable