Aspects of human nature further complicate matters: Well-intended managers resist any notions of “their people” doing “bad things.” They screened them. They hired them. They work with them side-by-side and – if they’re good bosses – have developed a genuine interest in their career development and even personal happiness. In addition, one of the most critical elements in building a high performing team is trust, so anything tha t can have a negative impact on that trust needs to be very carefully analyzed and explained before being implemented. This disposition is not about being gullible, we all have white hat syndrome at times. It’s about being a helpful manager – and a decent person.
But it would be imprudent to completely abandon a sense of cautionary oversight, as there has been a steady flow of news reports about insiders doing harm to their organizations. They range from probably the most notorious of incidents – Edward Snowden’s carefully plotted leaking of sensitive NSA documents after downloading 1.7 million files – to possibly the funniest (except for the company in question): A software developer for a U.S. critical-infrastructure company literally outsourced his job by sending his log-in credentials to a Chinese contractor, so he could get paid six figures to surf Reddit, post Facebook updates, shop on eBay and watch cat videos all day2. While the latter anecdote has generated considerable amusement, it underscores the reality that internal threats pose serious risks: 53% of organizations have experienced an insider cybercrime incident, according to the 2013 U.S. State of Cybercrime Survey from the CERT Insider Threat Center at the Carnegie Mellon University. So who are the users who pose threats? In all cases, they have authorized access to the network and their co-workers and managers are usually shocked that they would do such a thing. Clearly, tech departments need the support of their leadership to do what plant managers and foremen did in the 1950s: Watch. Audit. Intervene. Prevent.
Regardless of the user’s full time or contractual status, you want to look for classic “tip-off” behaviors which can lead to trouble, e.g. the clear taking of proprietary information  without need or approval; expressing increased interest in matters unrelated to defined duties; and connecting to the network remotely from unusual places at unusual times, having access to machines that they really don’t need access to, constantly seeking for elevated privileges, to list a few examples from the FBI profiling studies. Without a program in place to stop these individuals, organizations stand to lose an estimated $412,000 on average per incident.
In many organizations, a “we trust everyone to do the right thing” mindset too often prevails, and data points abound, such as 50% of employees who leave a company admitting to taking proprietary data, to show why this is highly questionable logic.
Another issue is with internal rule benders who conclude that the added layer of protections are either unnecessary and/or overly alarmist and/or present too many inconveniences for them to deal with. They consider themselves and their work as above it all, and decide on their own as to when to follow security protocols – and when to circumvent them. As they grow more comfortable with the latter, they choose it as their “default” setting, doing things such as sending proprietary information outside the company “walls” without encryption, logging onto systems that they should not have access to, elevating other person’s access rights because security doesn’t understand the person’s real need, etc. They love external drives and USB sticks, because these tools make it nearly impossible to distinguish risky behavior from harmless, work-related shortcuts. In fact according to a recent survey conducted by Voltage Security 50% of network users admitted to having bypassed security controls to complete a task more quickly and easily. Internal Rule Benders make up 15% of treat actors who have caused or committed a breach of their organizations’ data. Senior executives are disinclined to acknowledge that the worst is, indeed, possible: “We trust the people we hire” and they perform a valuable role. We do not want to promote a culture of suspicion. These Senior executives need to realize that Trust but Verify is a good mantra for them to start living by.
 It’s too difficult. It’s too costly. There’s no imminent crisis. “Status quo” is working out just fine. Then like, Target, Home Depot and many others they find out that it’s not, after it’s too late.
On our team how can we implement items that allow us to do the following?
- CERT’s “Common Sense Guide to Mitigating Insider Threats” has emerged as an industry standard for program implementation. Among its recommended actions:
- Launching a security information and event management (SIEM) system to log, monitor and audit user activity.
- Detecting activities outside the users’ normal scope of duties via phone/network logs, etc.
- Regularly reviewing accounts to verify that all are still active and necessary.
- Ongoing auditing of user accounts created and passwords provided.
- Requiring all system administrators to change passwords when a fellow administrator leaves his or her job.*
- Monitoring and controlling remote access from all end points, including mobile devices.
- Incorporating threat awareness/prevention policies into comprehensive termination policies.
- Developing a baseline of “normal” network device behaviors.
- Inventorying IT assets and routinely assessing their present-day role and relevancy.
Remember:
If you don’t go looking for trouble you will never find it.
But, Trouble will find you / your Organization
How do we get back to this future in a technological workplace?
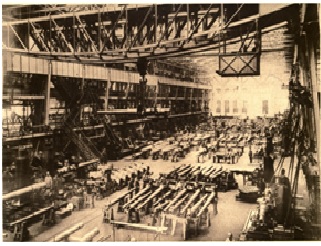
In the classic factory of the 1950s, managers strolled from their offices on a floor that towered over plant activity, closely observing whether shift crews below were doing what they were supposed to do. Because employees knew the eyes of a supervisor may be upon them at any time, they were less inclined to cheat the system – such as slipping any of the company’s property or product into their pockets, or sabotaging a machine out of spite. Thus, the business was protected. And what was good for the business was good for everyone involved: the bosses, the investors and, yes, the workers. Said another way, it is good for business and for organizations to keep one rotten apple from spoiling the bunch.
 Successful ransomware attacks are at an all time high, we are losing the cyberwar, cyber criminals are making more money than ever before and it is only going to get worse, a cyber attack could be as damaging as a nuclear war – the headlines abound with comments such as this. Yet, there are still a lot of postings about how information security should not be the office of No. Really? Information security is a security function, as an information security professional are you really going to say – Yes, sure, go ahead and port that un-scanned software code into our production environment? I would hope you are going to say no you cannot port that un-scanned software code into our production environment. No is not a bad word, it is one that the job requires us to say. If you are offended when someone says you are the office of No- don’t be. To be a security professional no is a good response. I train my team members to say “yes, but” in order to soften the perceived impression of the word no ….. (here’s a clue – “yes, but” is still a no – no matter how you spin it).