The Office of No, Really?

No  Successful ransomware attacks are at an all time high, we are losing the cyberwar, cyber criminals are making more money than ever before and it is only going to get worse, a cyber attack could be as damaging as a nuclear war – the headlines abound with comments such as this.   Yet, there are still a lot of postings about how information security should not be the office of No.   Really?  Information security is a security function,  as an information security professional are you really going to say – Yes, sure, go ahead and port that un-scanned software code into our production environment?  I would hope you are going to say no you cannot port that un-scanned software code into our production environment.  No is not a bad word, it is one that the job requires us to say.   If you are offended when someone says you are the office of No- don’t be.  To be a security professional no is a good response.  I train my team members to say “yes, but” in order to soften the perceived impression of the word no …..  (here’s a clue – “yes, but”  is still a no – no matter how you spin it).

However,  I have yet to sit in a business meeting and see any of my peers simply say no without being willing to engage in dialogue that would lead to a good and secure solution.   So for those who don’t like to say no then do it this way – yes you can put that server with 2 catastrophic exploitable vulnerabilities into the environment after we help you remediate the vulnerabilities or work on additional adequate controls that will allow us to use the server in a safe and secure manner.    For me, information security professionals can and should say no,  but after doing so we need to be helpful and smart enough to engage in conversations that help the business figure out how to do what they want to do in a way that is cost effective, safe and secure.

In many ways with the types and amount of successful attacks we are experiencing across the U.S. infrastructure being the office of Yes is a far more scary response than saying No to items that put your business at risk.

Critical Manufacturing Legacy Systems


     One common item that information Security Professionals working in Critical Manufacturing environments have to deal with is that of legacy systems. You see, in Critical Manufacturing environments it is very common for the systems that run and control factory lines to remain in place for a very long time. Some of these systems can be running Operating Systems(OS) that are 10 to 15 years out of date. In many cases these OS are no longer vendor supported and cannot be patched to remediate known exploitable vulnerabilities. These older systems are often used to run production lines and they still do a great job at doing what they were purchased to do.  It is difficult, rightly so, to convince the leadership team at a factory to spend money to replace something that is old but that is still doing the job it was purchased to do. It cost money and reduces potential profits to replace these old and outdated systems with new systems.  Because they continue to do the job they were purchased to do justifying the new spend can be a difficult thing to do.   

     From an Information Security point of view these systems pose a large risk to the overall manufacturing environment and if hacked could cause a large scale production outage.  In smaller companies this type of major Cyber attack can result in no longer being able to conduct business and permanently closing the doors.   Legacy systems that are commonly found on the shop floor are often 3, 4 or even 10 years out-of-date when it comes to standard Information Technology patching.  Information Security Professionals look at these systems as attack vectors while the people working in the Critical Manufacturing environment view them as cost effective work horses that are getting the job done. While cyber attacks on networks at Sony, Target, Home Depot and the US Government are getting all the press, the greatest cyber vulnerability is in manufacturing. “By raw numbers, and by the numerous manners of attacks, manufacturing is the most targeted area now, even compared to financial services,” Chet Namboodri, senior director of Global Private Sector Industries at Cisco, told Design News. “Financial services gets more press, but industrial networks get more attacks.” Attacks and warnings such as Stuxnet, Armaco, SolarWorld and U.S., Steel to U.S. regulators and security experts sending out an official warning that hackers could now access critical medical equipment including pacemakers and insulin pumps with potentially deadly results make the threat to Critical Manufacturing a real one.  Determining what to do in order to lock down and protect the Legacy systems while at the same time allowing them to continue doing the work they have been doing is a  major part of an Information Security professionals job.

     “You can’t scan that system (or you can’t put AV on that system) because it is old and fragile and if you bring it down we will not be able to produce our product”  Is way too common of a phrase in the Critical Manufacturing environment. In many cases Information Security Professionals are asked/told to please just leave the systems alone, do not run vulnerability scans, do not put antivirus on them, do not put a light firewall on them, do not patch them, do not put updates on them, etc.  This type of thinking by Information Technology and Factory leadership teams is shortsighted and is putting their entire production capability at huge risk of catastrophic failure.  As these legacy systems are outdated and no longer being supported by the vendor they are hugely exploitable to any blackhat or hacker that wants to take advantage of their exploitability. The reality is that the risk is real,  the risk is great and from past events we know that these systems pose easy to use attack vectors for blackhats, fraudsters and competitors seeking to cause negative business impact to the company.  

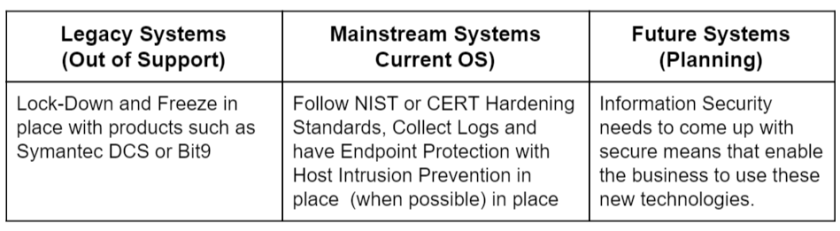
     Information Security professionals working in Critical Manufacturing should take the approach shown in Table 1 for dealing with the Computer Systems residing in the factory environment and that are on the plant floor.  By following this methodology the legacy systems will be protected while at the same time be able to continue doing the job they are good at and that they were purchased to do.  In most cases this approach will also reduce the overall risk that these systems pose to an acceptable level.

Legacy TableTable 1

This approach when combined with the network segmentation and smart firewall approach discussed in my previous blog on Critical Manufacturing is the start of a successful recipe in securing a Critical Manufacturing environment.

Information Security Defense in Depth Part 2 – A Bit More Technical View

Still for foundation level folks but a bit more technical view of Defense in Depth than last week’s post.


Critical Manufacturing Cyber Security Defense Program – A Starting Look

Cyber security professionals  are often tasked with trying to defend more than they have the resources to defend. This is especially true in the area of Critical Manufacturing as there tends to be a strong desire to protect everything.  In many cases when we try to protect everything we end up protecting nothing.  A Cyber Security Defense Program (CSDP) needs to be very focused and strategically deployed to protect the systems and areas which need protected.

Critical Manufacturing as defined by the Department of Homeland Security(DHS) is primary metal, machinery, medical, electrical and transportation.   Primary metal is Iron, Steel, Aluminum non-Feros metals;  medical includes facilities and devices, machinery is engines, turbines and power transmission, within electrical is electrical equipment manufacturing, transportation is :  vehicle, aviation and aerospace parts and vehicle manufacturing and railroad rolling stock.   Products made by these are essential to critical infrastructure sectors. The Critical Manufacturing sector focuses identification, assessment, prioritization and protection of nationally significant manufacturing industries within the given sector that may be susceptible to manmade or natural disasters.  This area is one that is critically in need of a strong CSDP.   The discipline for CSDP must not be twisted to taint what should be a strategic approach to the industrial base (“Critical Capabilities At Risk,” 2009).

One critical component to the protection of a Critical Manufacturing environment is that of using next generation, aka smart, firewalls with intrusion prevention and with some form  of malware  prevention and detection, updated via global feeds, enabled. This firewall environment should be set up in such a way as to segment the Critical Manufacturing infrastructure. Each individual plant or factory within the Critical Manufacturing environment should be on their own local area network (LAN) segment. A very basic way of thinking about this is captured in Figure 1 below.

Manufacturing Network Segmentation

Figure 1

Because of the method in which business decisions are made for factory systems it is critical that organizations involved in Critical Manufacturing use strongly firewalled network segmentation methods to ensure that each of their factory sites sit behind their own firewalls and on their own network segment (DHS, 2009).  This allows better control of the environment and enables the isolation of one factory without impacting the rest of the factories owned by the organization.  In this way if one factory is compromised by a hacker or group of hackers it can be removed and isolated from the organization’s global IT infrastructure.  Network segmentation, also called Network Control (NC) is a primary bastion for a defense in depth strategy and it can also be used to help prevent a blackhat from pivoting from a relatively unsecure factory system to a core business system.  Combining an Intrusion Prevention Appliance (IPS) or functionality with the firewall inside of a network segment provides a strong front line of perimeter defense for factories involved in Critical Manufacturing.  These IPS’ do not have to be overly tweaked and analyzed to be effective, running them in default signature mode is an adequate layer of defense for the network segment protecting and controlling a factory environment (DHS, 2009).

A Note I Wrote to Someone Who Once Worked for Me

I recently had the honor to help provide a strong reference for a person who worked for me as a Cyber Analyst.  She got the Senior position she was going for but was just a little worried about what they should do in order to lead a team and be a good leader.  Here is what I related to this extremely competent future Cybersecurity leader.

Hi:

First and foremost – you are going to do great in your new role. I encourage you to model your leadership style after the following rule(s):

Use the leadership model of:
Am I doing the right thing
Am I doing it for the right reason
Am I doing it at the right time
Am I doing it in the right way

This is on the back of the Challenge Coin I had made up for our UC team.

Always act with Integrity and walk your talk. You don’t always need to be right but you always need to be honest with the people you lead.

Remember that “We are smarter than Me” and foster healthy discussion and debate on topics. Try to pull ideas and suggestions from those you lead who are more on the quiet side. Don’t let aggressive Type A personalities (like me) dominate the conversation.

When coming out of a meeting get your team members used to doing a 5 minute feedback session (what did we do right, wrong, what should we (or I) have done differently, etc. Remember – Feedback is a gift.

Training of your people needs to be a priority and always remember to help others be Greater Than Yourself. There is enough success out there for everyone, help grow your people so that they can be your boss some day and if that did happen they would be a good boss to work for.

Don’t hesitate to email if you have specific questions. Have confidence, breath deep and believe in yourself – you got this!

Your Horse Was Analog

Your Horse Was Analog

Kevin L. McLaughlin

A  speech I made to 350+ people at the Michigan joint Military Ball.  Amway Grand Plaza Hotel.

Like my tie? My wife didn’t – gave me a lot of grief before we left the house,  you know how difficult things can be when your significant other doesn’t approve of your choice in clothing.

Well you see this tie has snoopy, the moon, the space shuttle and Apollo craft on it and it was given to me by Fred Hayes, yes the Apollo 13 Fred Hayes , yes astronauts are pretty neat people,  anyways Fred gave this to me when we were working on a project together and he told me that whenever I wore this tie I could look down at the pictures and that no matter what I do in the life I should remember that if we put a man on the moon we can do anything as a country.

…. as a country we can do anything,  even figure out how to defeat this cyber threat.

I want to change that thought just a little bit because I know what type of people went to and walked on the moon –  as a whole the U.S. Military and its veterans can do anything   make no mistake we are under attack, not by conventional weapon systems like guns and missiles but by cyber warriors utilizing digital attack vectors.

My speech tonight will be about trust and how it will help us win our cyber battle.  But, before I start I would like to do a shameless plug for the Whirlpool Veterans Association, who mentors soldiers transitioning to the private sector and with multiple outreach programs – I am sure many of the companies you work for have similar programs and a big thank you to those as well.

Trust and authority will be tonight’s theme. A lot of Information Security Professionals left Home Depot after years of not having their voices heard and repeatedly being over-ridden about whether a system could be touched or not.  Many Board of Directors are asking how to fix the cyber issue  –  a lot of the CIO’s and some of the CISO’s when asked that question are taking a passive posture of saying that their job is to make them aware of the risk versus telling them what to do.  In my opinion that is not the right answer… the people who are trained in cyber defense need to drive answers and solutions not just show risks

I will admit though that this morning while I was working out I had a big moment of angst,  you see I am an expert in this field and I can have an opinion and if I get it wrong a company will lose money but you know – if you get it wrong  lives will be lost and in the worst case our Homeland can fall.  Even with that – tonight you will hear what I feel we need to do in order to start winning the cyber battle.  We got our butts kicked by the bad guys in 2014 and it was a loud wake up call to anyone paying attention that what we have been doing is not the answer.

The general theme throughout my speech tonight will be one of trust. High performing teams consist of players that trust each other and who understand that each of the team members has an area that they are the expert in.  We cannot continue to ignore or muffle the voices of our highly trained and skilled cyber defenders and expect to be successful in our cyber defense efforts.

One of the first things we need to understand is that there is always in existance a large understanding gap.  I got my first taste of this type of understanding gap when I returned from Basic Training and I was talking to my Grandpa.  He asked me where I was stationed and I said Fort Bliss Texas,  he asked me what units were stationed there and I said the 3rd Cavalry. He got excited and we started talking;  about 5 minutes into the conversation it dawned on me that he was talking horses and I was talking tanks.  He was talking analog.

You see, we continue to increase our combat effectiveness by implementing new tools and technologies the majority of which are not analog, but are instead digital.  Digital means that they present entirely different attack vectors and will require us to have an entirely different level of trust in the expertise of the cyber defenders we put in place.  We must protect our digital assets.

The current generation of service men and woman are some of the first who have known nothing but digital tools.

(I left out this next part due to time constraints)

[Did anyone see the movie BattleShip? It’s a bit of a cheesy movie but there is a part in it where the modern digital destroyer gets blown up and the only available ship to fight the aliens was a WW II BattleShip,  they are working to try and figure out how to use the ship and the Chief looks at the Ensign and says “sir, this old thing is completely analog, it will take us years of reading the manuals to learn how to float and fight it”.  All of a sudden a long line of navy veterans come walking up and they are able to work side by side to show the team how to run and fight the ship –  think about this – in another 10 to 15 years people who understand analog are not going to be around to help us out.  ]

I continued my speech here —    I have to wonder how many of these digital troops would use a smartphone or GPS, even if disallowed in the mission parameters,  if they get lost during training?  I’m not disparaging anyone, I just realize how very hard it would be for any level of team leader to stop themselves from using an alternative before calling into command and telling someone that they were lost.  We all know how difficult that radio call would be to make.

What is scary is that if these digital devices were suddenly taken away our combat effectiveness would be greatly impacted – maybe by 90% or greater.  Ok,  each of your digital devices, smartphones, etc. have just been reset to 0:00 – how many of you can tell me what time it is?  Show of hands  {note – out of 350+ people in attendance only 2-3 raised their hands} wow, that was actually far worse than I expected it was going to be.

Having these digital items give us a significant advantage but also put us at risk if we don’t adequately protect them from cyber attack.  Tanks, Planes and ships will not operate if their computer systems are taken off-line.  Year after year we see annual reports that tell us  that our military systems are in no better shape than private sector systems are and our military IT staff feels the same pressures to get systems in place quickly rather than securely – we must be better than that. {looked down at tie and lifted it up}  We can do anything….

Most of us Cybersecurity professionals (risk professionals, assurance, etc. ) are very passionate about what we do – I personally spend upwards of 30-40 extra hours each week staying current, learning, wargaming, gathering intelligence, figuring out business enabling security strategies, and more.

How many of you in this room (Cybersecurity men and women you are not allowed to answer) can say you spend that much time studying and focusing on cybersecurity? How many of you even spend 2 hours per week?  Of course you don’t spend time studying Cybersecurity nor should you – that’s why you put cyber security professionals on your team.

Then why is it that across Corporate America, and I can only imagine it is a bit worse in the military, is it so hard to build trust between the Cyber defenders and the management community of the organization?  I know some of you are sitting out there thinking -What’s this guy talking about – I trust my Cybersecurity person.  Do you?  Do you really?

Think about this … you are the Colonel in charge of finance imagine an E6 Cyber defender walking into your office at month end closure and telling you that he has to take one of your business critical system off-line immediately for security patching as it is critically exposed and can be very easily compromised which could put the rest of our infrastructure at risk. He then tells you that the outage may last 8 to 10 hours.    Well, after 17 years experience as a security professional in Corporate America I can tell you that this request would be met with a lot of resistance and most likely the Cyber Defender will be told to wait for a day or two to do the patching.   Often times that directive will come with a comment about “you security guys and girls don’t really understand the business and tend to over-react”….

Hmmm…  I can only imagine similar conversations happening inside of Target, HomeDepot, Sony, Subway, Dairy Queen, Sigh, I’m not going to name them all – but like I said earlier we really got our butts kicked in 2014.  2015 continues the theme with the Anthem breach – a breach which directly impacts each one of you the Feds feel China committed the breach to continue their mission of gathering the personal data of our active and former military and their dependents.  We don’t know what they want the data for but it is obvious that they want it

Trust,  Target has a 148 million reasons – those are dollars by the way – plus open lawsuits, HomeDepot has 120 million reasons and Sony has 1 billion reasons, to implement a Cyber Defender authority policy.   1 billion?  how many of you work for companies that would even be able to survive a 1 billion dollar loss? I imagine if I lost a billion dollars for a company I’d be out on the street. and luckily for us we are starting to see Board Chairman, CEOs and CIOs resigning due to allowing a security breach to occur on their watch. Why is that lucky?  because it might raise the awareness we need to help fix this issue.

A base level of trust needs to be in place that makes it so that is assumed your cyber defender, who also is part of your profit sharing plan and wants the company to make money or who is a strong patriot and wants our tanks to run or planes to fly,  is not going to willy-nilly.  I just wanted to say willy-nilly in a formal speech,  is not going to willy-nilly take systems off-line and that when they say a system really needs to be fixed immediately they need to be granted the authority, we already give them the responsibility and career risk when a breach occurs,  now let’s give them the authority they need to protect the organization,  even if there is a small short term negative profit impact – wow that is hard to say but I bet if we asked Target, HomeDepot, Sony, Anthem, you get the idea if they could go back in time and accept a $5,000.00 profit hit in order to take a system off-line and patch it instead the breach they would all say yes.

For you the risk of allowing the E7, E8, Lt. Captain, Major, etcetera, I’d try to go on but I’ve been out of the military for a loooong time and would most likely get the other command ranks wrong…   to trump the cyber defender may just result in a significant loss to both your combat effectiveness and your ability to defend our country.

Trust,  trust the cyber defense experts that we are graduating from our military schools to both understand the business and to effectively assess the risk and make the call on fixing open and exploitable channels of attack.  While the department heads and commanders should still have the final say an answer of “don’t touch this system” or an answer of “you are over-reacting to this threat  – yet how would they even have the expertise to make that judgment?  should be the rare exception and not the norm.       – Trust and authority-   we can win this cyber war and defend our systems against the cyber threat.
Home Depot Breach 43M loss posting on LinkedIn

I just read an article on LinkedIn about the negative impact caused by the recent Home Depot breach. Here are my thoughts about how all the 2014 breaches should change some C level and Information Security paradigms. These could cause a major C suite thought shift and maybe even a large paradigm thought shift in how our profession thinks about the skills and talents really needed by Information Security professionals.

Note – I know this opinion will not resonate well with some CISO’s – Major IT departments continue to hire CISO’s that have little to no security background. Hackers and blackhats are associated with organized crime and IMO until we put more of an emphasis on the word SECURITY in the CISO title and until CISOs stop walking a tightrope by always trying to compromise and keep the business happy by letting the business need trump the security need (“ok, don’t patch that extremely vulnerable system I understand your business need not to” ) the crooks will continue to win.

Also, it appears that too many companies are basing their CISO hiring decisions on the candidate’s business acumen. Wouldn’t it be better to focus on how well the candidate knows how to fight and deter criminals?
I’m not saying CISO’s don’t need to understand the business I am saying that a stronger focus should be on how much the CISO knows about criminals and crime fighting. I also realize that thought would take a major paradigm shift in the thinking of the C suite.

The Cyber Security CIA explained via Calvin and Hobbes

Leave it to my son Kody, who is starting his Cyber Security career to come up with this novel way to explain the CIA triad for Cyber Security.

In InfoSec terms, CIA refers to Confidentiality, Integrity, and Availability. To illustrate how these principles work, let’s look at Calvin and Hobbes.

Calvin and Hobbes create a club called the “Super-Secret-No-Icky-Girls-Allowed” club. During their very first treehouse meeting, they draft a document entitled “member list” and write the names “Calvin” and “Hobbes” on the list. This list is the club’s most valuable asset so Calvin and Hobbes need to maintain the CIA of the asset. The confidentiality of the list is critical as the exposure of the secret member list would cause the entire super-secret club to lose its purpose. The integrity of the list is also important to ensure that unauthorized modifications of the list can’t be made. It would be terrible if Susie’s name were to make it on the list of if Calvin’s name were to be removed. Lastly, the availability of the list is important. When the club meets to have their secret meetings, they need the list do roll call and to ensure that those in attendance are listed.

So now that we’ve got the idea, we can explain how CIA works for business assets. The confidentiality of the asset is necessary to ensure that only those with appropriate privileges and appropriate need can see the asset. The integrity of the asset is necessary to ensure that the data has not been changed and, if it has, a log of changes is kept. The availability of the asset is necessary because it is not of any value if no one can interact with it for its intended purpose.

Compliance does not Equal Security

When I read items like this:

Agarwal said NoMoreRack is now in the process of certifying itself this time as a Tier-1 merchant, even though the number of credit and debit cards it processed in 2013 placed it squarely in the Tier-2 range.

I get frustrated.  While I understand that Compliance is necessary and is important companies still need to understand that being compliant does not mean you are secure! There is more to it than that.  In too many cases Compliance is just a check box that makes senior management feel better about the overall state of organizational security.

Fun Story about UC Cyber Warfare Game

Ok, so I wasn’t going to share this but I sort of think its
pretty neat. My friend Quinn and I started an urban legend story at
the University of Cincinnati from my classes first cyber warfare
event years ago. One of my current students just posted the following item in a class I am teaching. This is a story that is really about the first
Cyber Wargame that I ran at UC as part of my Information Security
Course. Quinn was the defender and I believe Karl Hart was the
attacker – it was a great event. What is even greater is that is
has now taken on UC “legendary” status. :-)
============================================

I am reminded of a story my Computer Networking teacher, Mr. Tom Moore, gave to us one day in class. He spoke of a game they played, I dont remember whether it was at UC or his workplace, but he said that they would divide IT professionals into 2 teams, one “hackers” and one that
protected data. He was on the hackers team. Well the protectors
were allowed a certain amount of time to design security for the
system they were trying to protect, and there after the hackers got
their shot. Well the hackers tried and tried to break the security
through their hardware but to no avail. Finally, Mr Moore was on a
break and happened to walk by the room the protectors were in (they
were set up in different rooms of a building) and realized no one
was in there. He tried the door but it was locked. However, another
faculty member, unaware of what was going on, walked by and Mr.
Moore asked her to unlock the door. She did and he notified his
team who came and stole all the equipment they had. They then broke
into the machine, got the data, and won. He used the Bill Gates
quote “if I can get access to your computer I will own everything
that is on it” and it stuck with me. This story is a prime example
of having physical controls in place, and not just one. It is
important to make sure your equipment and data are both safe from
harm.